Choose your seat at the table.
The same grade reads differently depending on the chair you're in. Pick your role to see what each score means for the work you actually own.

A board's job is governance. The grade tells you whether management is governing this risk well.
Great
Good
Needs Improvement
Immediate Attention
Failing
Your Score & Next Steps
One sentence per grade, plus the move that follows. Use this as the cover slide for your next board update, vendor review, or executive standup, the technical findings live underneath, but the grade is the headline.
Management is operating the company in a defensible posture, with software risk visible, monitored, and trending in the right direction.
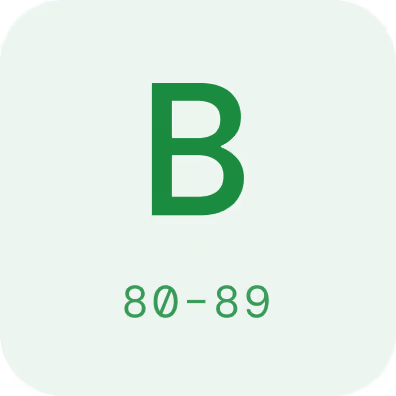
Posture is sound and the residual issues are routine, the kind of thing that warrants a brief mention in committee but no escalation.
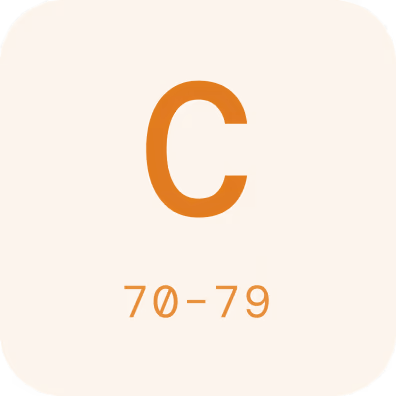
Real exposure is now visible to outside parties, and the board should expect questions from auditors, insurers, or major customers if it is not addressed.
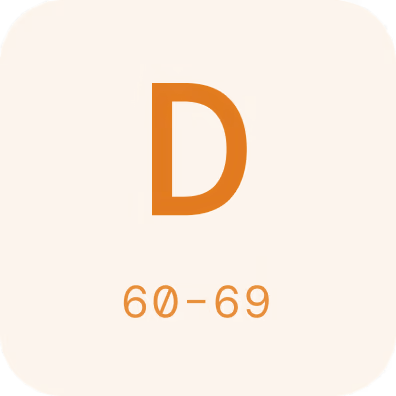
Findings at this level represent the kind of risk a board is expected to oversee actively, with a named owner, a timeline, and a status update at the next meeting.
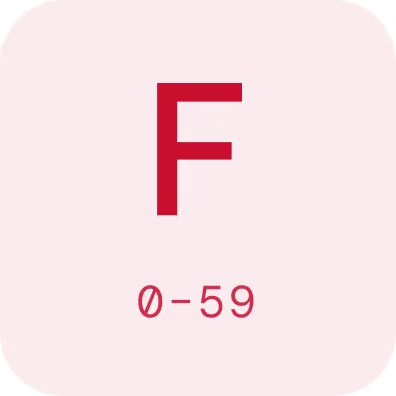
Exposure at this level is the kind that ends up in shareholder letters, regulatory filings, and litigation if left in place, and it requires immediate management response.
How the grade is calculated. The letter grade rolls up findings across all five External audit categories, exposed files, cookie and session security, SSL and TLS health, mixed content, and sensitive path disclosure, weighted by severity. The full technical report lives one click away for the engineering team.

Your security posture is a revenue and reputation asset. The grade tells you which one it is today.
Great
Good
Needs Improvement
Immediate Attention
Failing
Your Score & Next Steps
One sentence per grade, plus the move that follows. Use this as the cover slide for your next board update, vendor review, or executive standup, the technical findings live underneath, but the grade is the headline.
Your posture is something your sales team can lead with, your investors can see, and your enterprise prospects will reward in their procurement scoring.
You are in good shape with a small list of items to clean up before your next board update, fundraise, or major enterprise deal cycle.
These are the kinds of gaps that quietly extend deal cycles, surface awkwardly in investor diligence, and let competitors with better posture win on procurement scorecards.
This is the level where enterprise deals stall in security review, board members start asking pointed questions, and the cost of inaction is bigger than the cost of fixing it.
Exposure at this level is the kind that becomes the headline that follows the company permanently, and it should be the most important thing on your calendar this week.
How the grade is calculated. The letter grade rolls up findings across all five External audit categories, exposed files, cookie and session security, SSL and TLS health, mixed content, and sensitive path disclosure, weighted by severity. The full technical report lives one click away for the engineering team.

Operations runs the company's commitments to customers. The grade tells you whether you can keep them.
Great
Good
Needs Improvement
Immediate Attention
Failing
Your Score & Next Steps
One sentence per grade, plus the move that follows. Use this as the cover slide for your next board update, vendor review, or executive standup, the technical findings live underneath, but the grade is the headline.
Your software delivery is meeting the security expectations baked into your customer contracts and SLAs, with no operational drag on the rest of the business.
There is a short list of routine items to fold into your next operational review, none of which require a fire drill or pull people off priority work.
These gaps will show up as longer customer onboarding cycles, more frequent security questionnaire escalations, and recurring interruptions to the engineering team.
Findings at this level are the kind that put your contractual security commitments and SLAs at risk, and they need a named owner with a deadline this week.
This is a breakdown in your software delivery hygiene that exposes the company to incident response, contractual penalties, and customer escalations all at once.
How the grade is calculated. The letter grade rolls up findings across all five External audit categories, exposed files, cookie and session security, SSL and TLS health, mixed content, and sensitive path disclosure, weighted by severity. The full technical report lives one click away for the engineering team.

The grade is a leading indicator on revenue at risk, insurance premiums, and diligence outcomes.
Great
Good
Needs Improvement
Immediate Attention
Failing
Your Score & Next Steps
One sentence per grade, plus the move that follows. Use this as the cover slide for your next board update, vendor review, or executive standup, the technical findings live underneath, but the grade is the headline.
Your software risk is documented well enough to defend your cyber insurance renewal, your audit cycle, and your next round of diligence without surprise costs.
Residual risk is small enough that it will not move your insurance premium or surface in diligence, but worth retiring before your next renewal cycle.
These gaps are the kind that show up as longer sales cycles in your forecast, harder questions from your insurance underwriter, and downward pressure on diligence valuations.
Findings at this level translate directly into deals stalled in security review, insurance exclusions on renewal, and material findings in any diligence process you enter.
Exposure at this level creates quantifiable financial liability across regulatory penalties, insurance gaps, contractual indemnification, and lost enterprise revenue, all at once.
How the grade is calculated. The letter grade rolls up findings across all five External audit categories, exposed files, cookie and session security, SSL and TLS health, mixed content, and sensitive path disclosure, weighted by severity. The full technical report lives one click away for the engineering team.

Security is now a stage in the enterprise sales cycle. The grade tells you whether you will pass it.
Great
Good
Needs Improvement
Immediate Attention
Failing
Your Score & Next Steps
One sentence per grade, plus the move that follows. Use this as the cover slide for your next board update, vendor review, or executive standup, the technical findings live underneath, but the grade is the headline.
Your AEs can lead with this in discovery, hand it to procurement teams without escalation, and turn the security review stage into a competitive win instead of a stall.
Your team will pass enterprise security reviews without escalation, and the small open items will not slow a deal that is otherwise ready to close.
These are the gaps that quietly extend enterprise deal cycles by weeks, force AEs to escalate to engineering on every deal, and lose deals to competitors with cleaner posture.
This is the level where enterprise deals get held in security review with no clear timeline, and your forecast slips quarter over quarter without an obvious cause to point to.
Exposure at this level will fail enterprise procurement security reviews on contact, end deals in flight, and put renewals with security-conscious customers at immediate risk.
How the grade is calculated. The letter grade rolls up findings across all five External audit categories, exposed files, cookie and session security, SSL and TLS health, mixed content, and sensitive path disclosure, weighted by severity. The full technical report lives one click away for the engineering team.

Your security posture is a brand promise. The grade tells you whether you can make it publicly.
Great
Good
Needs Improvement
Immediate Attention
Failing
Your Score & Next Steps
One sentence per grade, plus the move that follows. Use this as the cover slide for your next board update, vendor review, or executive standup, the technical findings live underneath, but the grade is the headline.
Your posture is strong enough to stand behind publicly, in trust pages, in case studies, in analyst briefings, and in the security stories your sales team tells in the field.
You can speak confidently about your posture in customer conversations and analyst calls, and the residual items do not need to be part of the public story.
These gaps are the kind that contradict the trust messaging on your website, your trust center, and your enterprise sales decks, and they need to be retired before they undermine the story.
Findings at this level are the kind that surface in analyst evaluations, competitor takedowns, and customer trust conversations in ways the marketing team cannot spin around.
Exposure at this level is the raw material for the next breach headline, the next analyst downgrade, and the next angry customer post, and it requires a coordinated response across security and communications.
How the grade is calculated. The letter grade rolls up findings across all five External audit categories, exposed files, cookie and session security, SSL and TLS health, mixed content, and sensitive path disclosure, weighted by severity. The full technical report lives one click away for the engineering team.

Product is the promise customers buy. The grade tells you whether the promise still holds at the edges of the product.
Great
Good
Needs Improvement
Immediate Attention
Failing
Your Score & Next Steps
One sentence per grade, plus the move that follows. Use this as the cover slide for your next board update, vendor review, or executive standup, the technical findings live underneath, but the grade is the headline.
The customer trust story is consistent with what the product actually does in the wild, with no exposed surface that contradicts the security claims in your marketing or onboarding.
A small list of edges to clean up that belong in the normal product hygiene track, alongside accessibility and performance work, not a special program.
These gaps are the kind that make security promises in the product narrative harder to defend, and that prospects pick up on in technical evaluations and free trials.
Findings at this level will block enterprise procurement, force last-minute scope changes in big launches, and turn into customer escalations that pull product managers off priority work.
Exposure at this level is the kind that contradicts the core trust positioning of the product itself, and it has to be addressed before any new feature work ships to customers.
How the grade is calculated. The letter grade rolls up findings across all five External audit categories, exposed files, cookie and session security, SSL and TLS health, mixed content, and sensitive path disclosure, weighted by severity. The full technical report lives one click away for the engineering team.

Risk and compliance is the function that gets asked, in writing, whether the company is operating within tolerance. The grade is your answer.
Great
Good
Needs Improvement
Immediate Attention
Failing
Your Score & Next Steps
One sentence per grade, plus the move that follows. Use this as the cover slide for your next board update, vendor review, or executive standup, the technical findings live underneath, but the grade is the headline.
Posture sits cleanly inside the residual risk appetite the board has signed off on, with documentation ready for auditors, regulators, and customer security teams.
Open items are small enough to live in the risk register as accepted residuals, with a review date and an owner, not as findings requiring action.
These gaps push you outside the residual risk appetite stated in your risk policy, the kind of variance that triggers a closure plan and a status update at the next risk committee.
Findings at this level qualify as material control gaps that have to be reported up to the audit committee, named in audit responses, and tracked to closure on a fixed timeline.
Exposure at this level represents a compliance breach that triggers mandatory regulator notifications, contractual disclosure, and the kind of formal remediation plan that goes on the public record.
How the grade is calculated. The letter grade rolls up findings across all five External audit categories, exposed files, cookie and session security, SSL and TLS health, mixed content, and sensitive path disclosure, weighted by severity. The full technical report lives one click away for the engineering team.

Every clause in your customer contracts assumes a posture you can defend. The grade tells you whether you can.
Great
Good
Needs Improvement
Immediate Attention
Failing
Your Score & Next Steps
One sentence per grade, plus the move that follows. Use this as the cover slide for your next board update, vendor review, or executive standup, the technical findings live underneath, but the grade is the headline.
Your posture supports the security warranties, breach notification timelines, and indemnification clauses already in your enterprise contracts, with documentation to back it up.
Open items are small enough that they do not affect your ability to sign customer contracts with security warranties or to defend your existing obligations.
These gaps are the kind that make contract security warranties harder to defend, BAA obligations harder to document, and breach notification timelines harder to meet.
Findings at this level put you at risk of being out of step with the security representations and breach notification timelines already written into your customer contracts.
Exposure at this level creates immediate contractual breach risk, potential regulatory liability, and the kind of evidence trail that surfaces in litigation and discovery.
How the grade is calculated. The letter grade rolls up findings across all five External audit categories, exposed files, cookie and session security, SSL and TLS health, mixed content, and sensitive path disclosure, weighted by severity. The full technical report lives one click away for the engineering team.

Every finding under the grade lands on an engineer's plate. The grade tells you how much remediation work just got added to the backlog.
Great
Good
Needs Improvement
Immediate Attention
Failing
Your Score & Next Steps
One sentence per grade, plus the move that follows. Use this as the cover slide for your next board update, vendor review, or executive standup, the technical findings live underneath, but the grade is the headline.
No new critical work is being created by this scan, the existing controls are holding, and the team can stay focused on roadmap features without a security side-quest.
A handful of low-severity items worth folding into the next maintenance sprint, none of which are urgent enough to interrupt feature work or page the on-call.
Findings at this level mean dedicated engineering hours to remediate, the kind of work that bumps lower-priority tickets out of the sprint and shows up on velocity reports.
These are stop-the-line findings that warrant a focused remediation push, pulling engineers off roadmap work until the exposed surface area is patched and verified.
Exposure at this level requires an immediate all-hands remediation effort, with code freezes on the affected components and a rollback or hotfix released before the next deploy.
How the grade is calculated. The letter grade rolls up findings across all five External audit categories, exposed files, cookie and session security, SSL and TLS health, mixed content, and sensitive path disclosure, weighted by severity. The full technical report lives one click away for the engineering team.