Built for the connected era

When everything is connected, you need one place to look.

AI is writing more of your code. Your software pulls from thousands of open source libraries. Your platform connects to vendors that connect to vendors. TripleKey gives leaders, boards, and customers the single source of truth that ties it all together.
CVEs · 2025
48,185

new risks published in 2025, roughly 131 every day

Third-party breaches
2x

third party involvement in breaches doubled to 30% of all incidents

Malicious packages
454,648

new malicious open source packages found in 2025, one new npm package every 6 minutes

Secrets exposed
28.6M

new secrets exposed in public code in 2025, with AI credential leaks up 81%

Built for the connected era

Software stopped being something your company writes. It is something your company assembles.

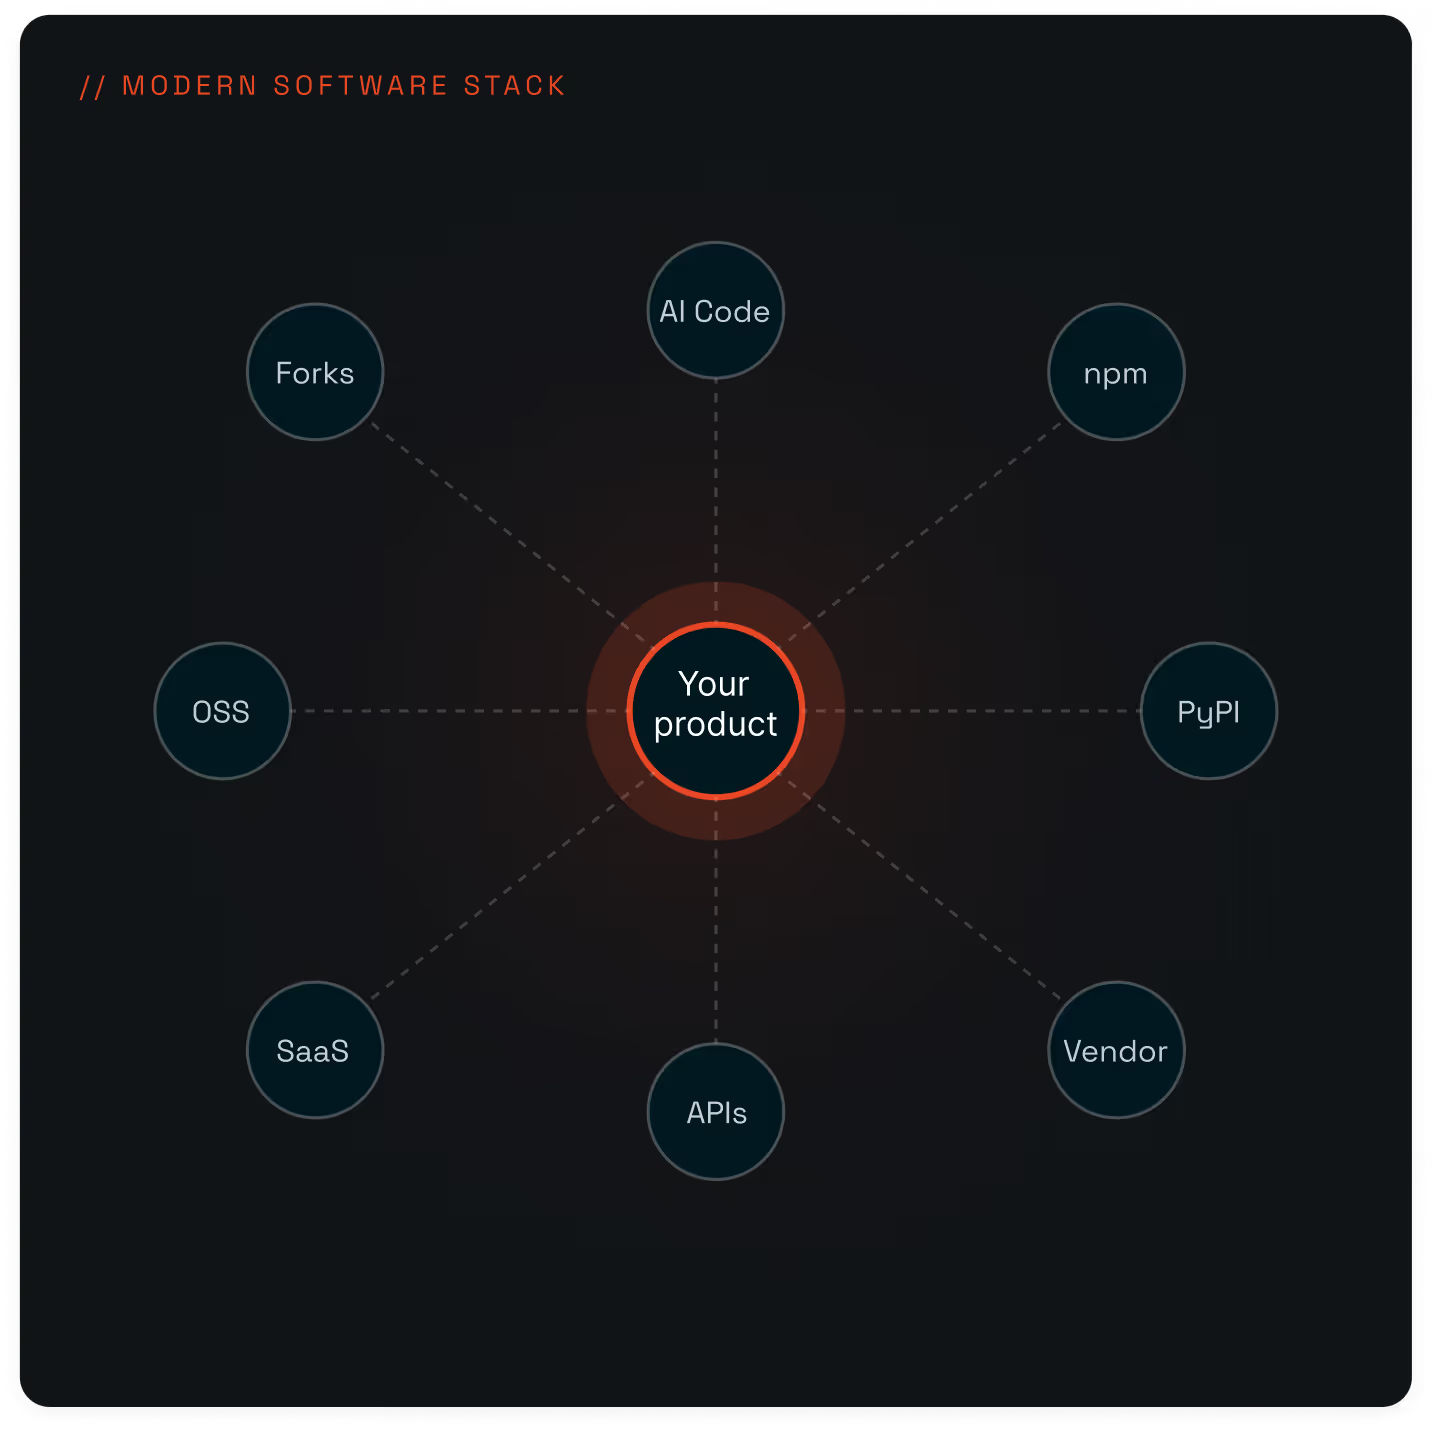
Modern software is a stack of borrowed parts. AI assistants generate code. Open source libraries do most of the heavy lifting. Vendors plug into other vendors through APIs. A typical product touches hundreds of components your team did not author and cannot directly inspect.

That assembly model is faster, cheaper, and more powerful than anything that came before. It also means a single weak link, anywhere in the chain, becomes your problem. Your risk is no longer just what you build. It is everything you depend on.

The old way of checking that risk, a once a year audit or a vendor questionnaire, was designed for a world that no longer exists.
Product architecture diagram
The four forces

TripleKey was designed for the way software is built today.

Four shifts have rewritten what software risk actually means. TripleScan was built for all of them at the same time.

The four forces

When everything is connected, every stakeholder needs to be looking at the same answer.

Boards ask one question. Auditors ask another. Customers ask a third. Engineers, executives, procurement, and compliance all need an answer they can trust, and they need to see the same number when they ask. TripleKey is that number.

How it works

We do not sit inside your engineering process. We sit beside it.

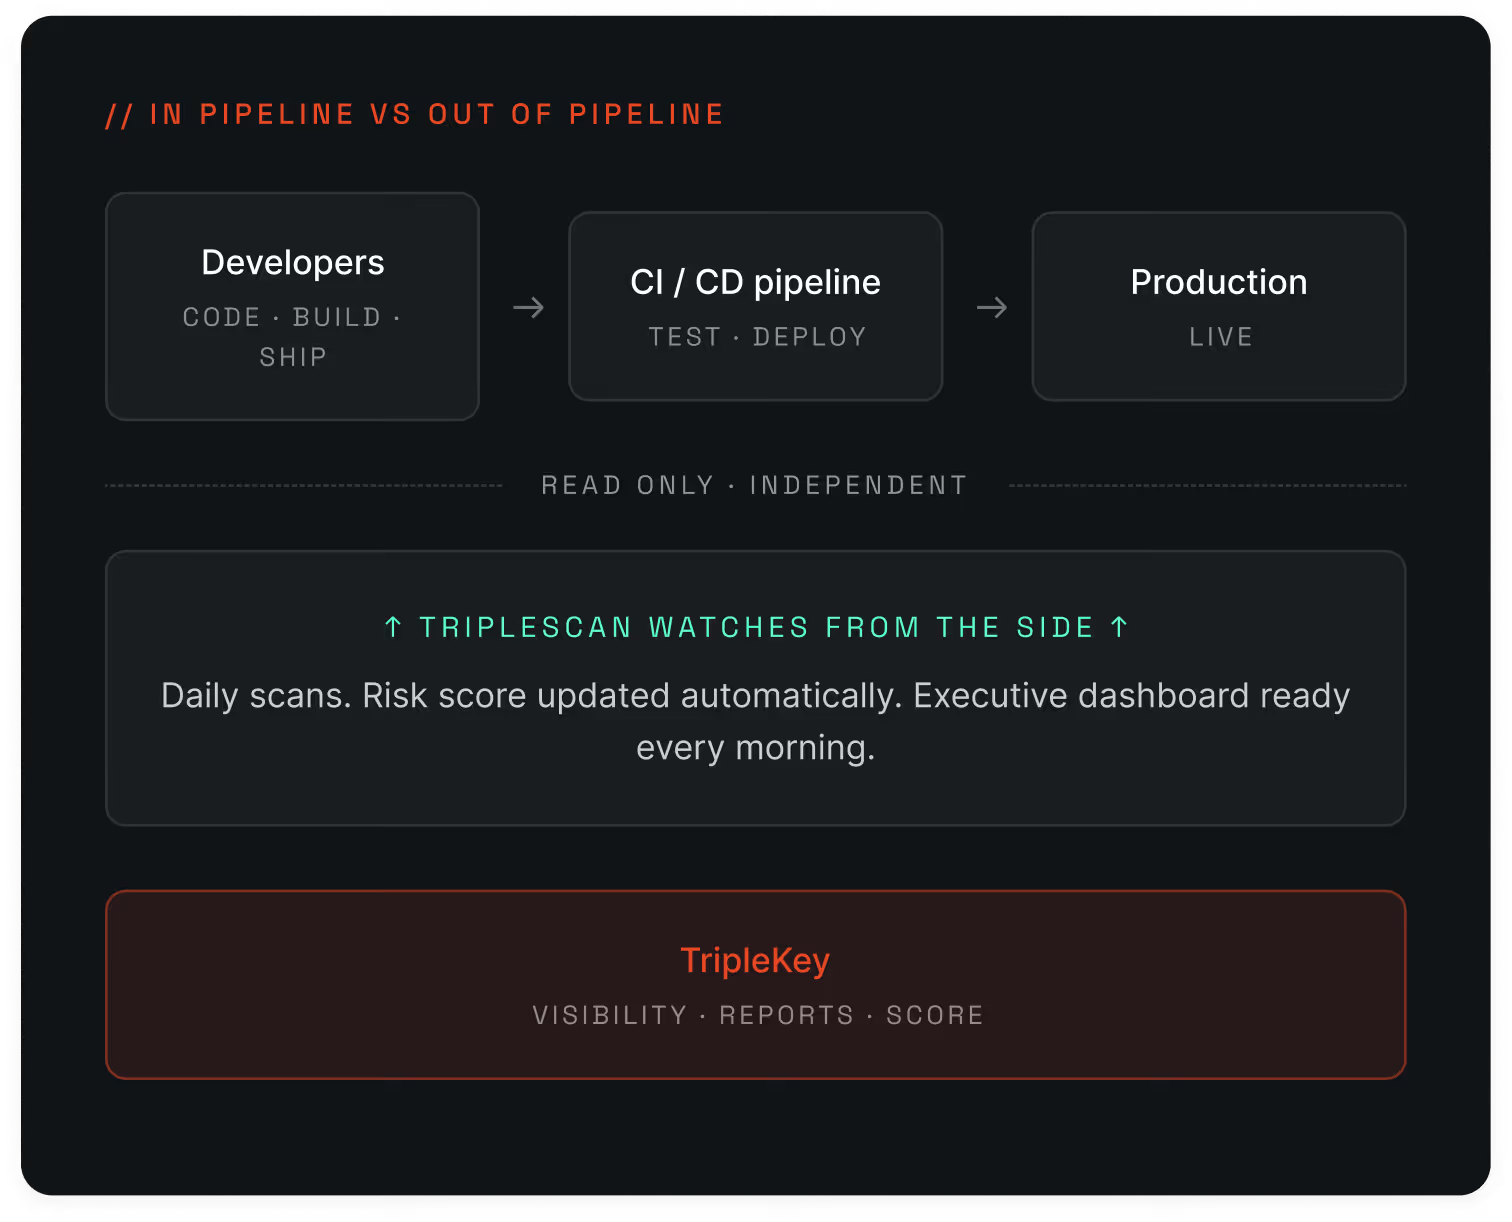
Most security tools insert themselves into the daily work of your engineers. They live in the build process, the code editor, the deployment pipeline. When they break, work stops. When they slow things down, deadlines slip. When they go silent, no one knows.

TripleKey works differently. We connect to your code in a read only way, the same way you might give a trusted advisor read access to a folder. We never touch the keyboard. We never block a release. We never change a single line of code. We look, we read, we report.

Your engineers keep moving at full speed. Your leaders, your customers, and your board get a clear, current picture of risk that updates every single day.

  • Nothing to install. Nothing to maintain. Nothing for engineering to babysit.

  • Cannot break a build, slow a release, or interfere with development.

  • Read only access. We see the code, we never modify it.

  • Stand up in days, not months. No procurement war with the engineering team.

Diagram of CI/CD and production pipeline with TripleScan monitoring read-only from the side
What changes for you

One source of truth. Everyone aligned. No one slowed down.

The point of all this is not a prettier dashboard. It is the operational change that follows when leadership, customers, and auditors all see the same answer.

White TripleKey logo mark
Get STarted TODAY

Stop relying on point in time audits and guesswork.

One platform. One score. One source of truth that everyone in your business, and every customer of your business, can rely on.

Logo icon